Okta Privileged Access Workloads lets CI/CD pipelines, infrastructure automation, cloud workloads, scripts, and AI agents authenticate using platform-signed OIDC tokens or managed API keys. This article explains workload connections, roles, policies, Principal SSH access, and secret retrieval, with a GitHub Actions lab demonstrating both SSH and secret reveal. It also covers static JWKS support for JWT workload connections.
Okta’s original agentic enterprise blueprint has grown into the Blueprint Alliance, bringing identity, cloud, AI, data, application and security vendors around a shared reference architecture. Here is what changed, how its four questions shape agent governance, and what architects should test before adopting the model.
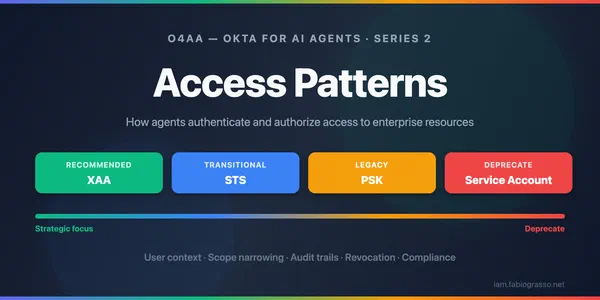
Protocol-level deep dive into the four Okta for AI Agents access patterns: ID-JAG token structure, sequence diagrams, audit log examples, and step-by-step Okta configuration for XAA, STS, PSK, and Service Account.
A strategic overview of the four access patterns for AI agent integrations — XAA, STS, PSK, Service Account — with a comparison matrix, decision framework, and migration roadmap. Companion deep dive covers protocol details and Okta configuration.
Who will guard the guards themselves? A critical analysis of vendor lock-in risks in IAM and the advantages of an agnostic approach based on Identity Fabric and open standards.
Analysis of 2024 banking cyber incidents (+45%) according to Banca d’Italia report and the Identity Fabric strategy for operational resilience in the Italian and European financial sector.